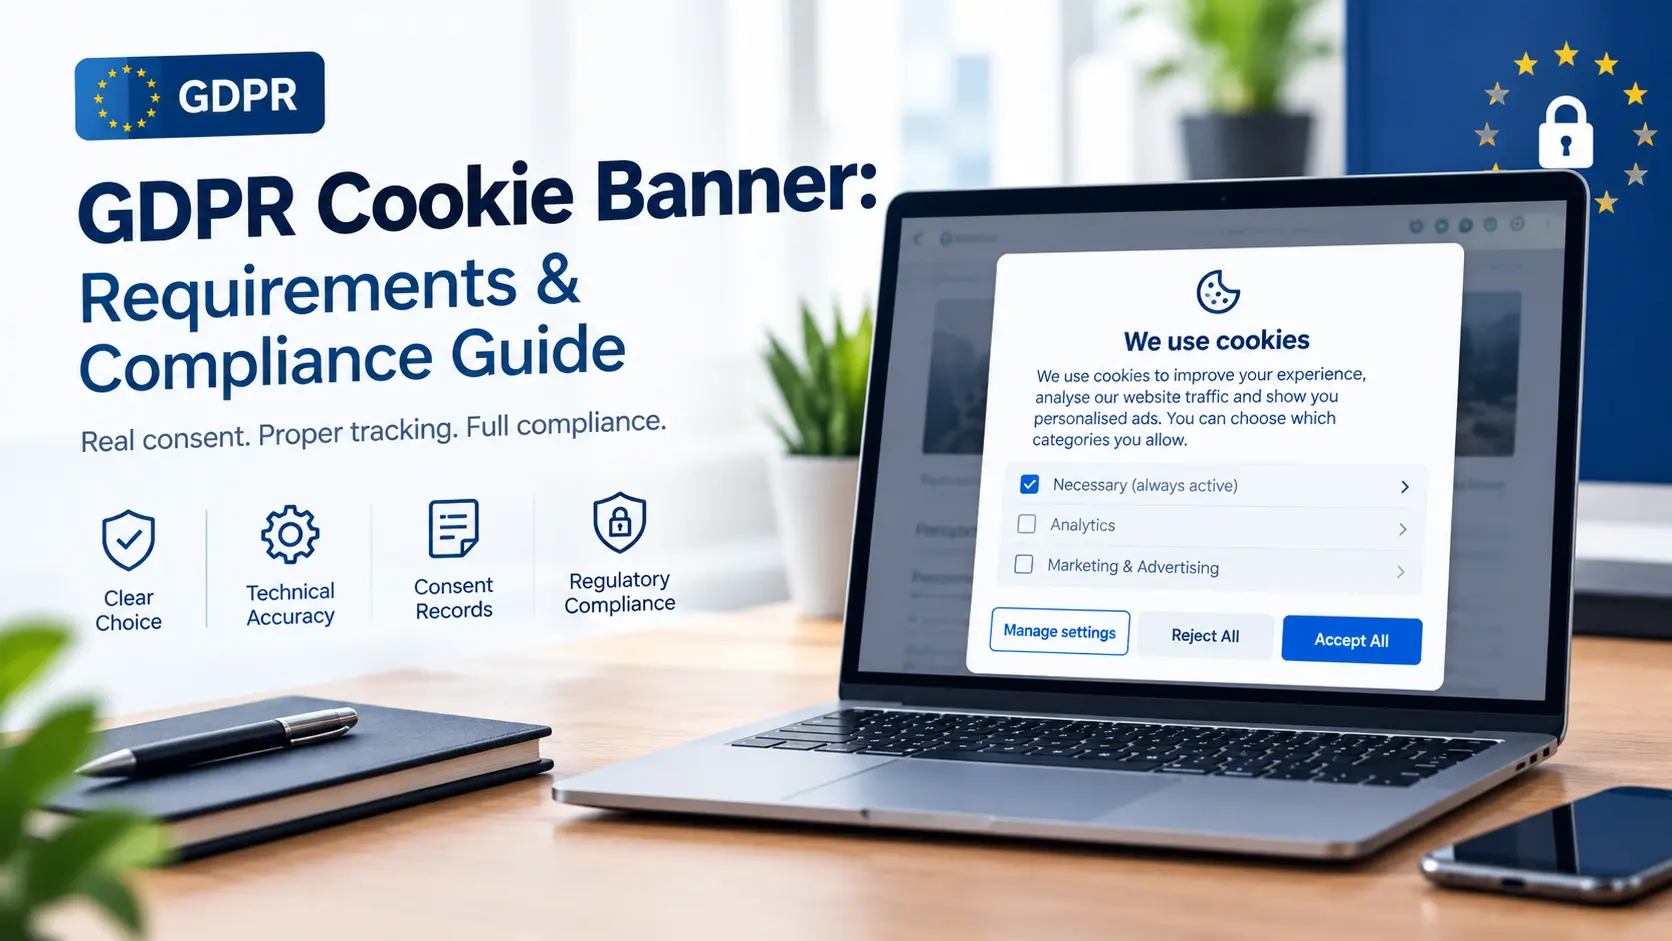
A GDPR Cookie Banner can look compliant while still collecting data too early. The bigger issue in 2026 is not whether a banner exists, but whether the website actually respects the choice shown on screen. Recent enforcement has focused on a simple test: can people refuse non-essential cookies as easily as they can accept them, and does the website wait for that choice before tracking begins?
This makes the technical setup behind a Cookie Banner just as important as its wording and design. We examine the key requirements, recent enforcement lessons, and practical checks businesses can use to test their Cookie Consent process.
What a GDPR Cookie Banner Must Actually Do
A compliant banner should give users a clear choice before non-essential cookies or similar tracking technologies are placed on their device.
Under European privacy rules, consent must be freely given, specific, informed, and based on a clear positive action. Simply continuing to browse does not create valid consent.
A practical banner should therefore:
- Explain that non-essential cookies are being used.
- State the main purposes, such as analytics or advertising.
- Provide a clear way to accept.
- Provide an equally clear way to reject.
- Let users manage individual categories where appropriate.
- Avoid placing non-essential cookies before consent.
- Provide a way to withdraw or change consent later.
For a broader explanation of privacy obligations, businesses can also review
The Overlooked Test: What Happens After the Click?
Many cookie reviews stop at the visible banner. That misses one of the most important compliance checks. We should test what the website actually does after each choice.
For example, suppose a visitor selects Reject All. The banner disappears, but an advertising platform still receives tracking data. The button may look compliant, but the underlying consent system is not.
The UK ICO’s current guidance says non-essential storage technologies should only be used after valid consent, unless an applicable exception applies.
A useful compliance test is:
- Open the website in a fresh browser session.
- Inspect cookies and other tracking technologies before making a choice.
- Select Reject All.
- Check whether non-essential trackers are still activated.
- Repeat the test with Accept All.
- Test the settings panel and consent withdrawal process.
This technical check can reveal problems that are invisible from the banner itself.
Cookie Banner Requirements for Clear Consent
The design should not push users toward acceptance. In December 2024, France’s CNIL ordered website publishers to change misleading cookie banners. Examples included hiding the refusal option, making it visually weaker, and presenting the acceptance option multiple times while showing refusal only once. CNIL stated that rejecting cookies should be as easy as accepting them. The European Data Protection Board’s Cookie Banner Taskforce also found broad agreement among European authorities that refusing or rejecting cookies should not be made harder than accepting them.
This means businesses should avoid designs such as:
- Accept All as a large button with rejection hidden in small text.
- A refusal link buried below several paragraphs.
- Repeated acceptance prompts with only one refusal option.
- Confusing phrases such as “Continue without accepting” when the actual choice is unclear.
- Pre-selected non-essential cookie categories.
A balanced design does not require every website to use identical colors or button layouts. Regulators assess whether the overall presentation is misleading.
GDPR Cookie Consent and Cookie Categories
A useful Cookie Consent system separates cookies according to their actual purpose.
Strictly Necessary Cookies
These support functions the visitor has requested or the website needs to operate, such as maintaining a shopping basket or certain security functions. Depending on the technology and legal basis, these may fall within an exception to the consent requirement.
Analytics Cookies
Analytics tools may require consent when they are not covered by a valid exemption. We should not assume that calling data “anonymous” automatically removes the need for careful assessment.
Advertising and Tracking Cookies
Advertising, profiling, and similar tracking technologies generally require particular attention because they can follow users across services or build behavioral profiles. Businesses should maintain an accurate record of which technologies belong to each category rather than relying on the default categories supplied by a Consent Management Platform.
Consent Records Matter Too
A banner does more than collect a click. Businesses may need to demonstrate how consent was obtained.
We recommend recording information such as:
- The consent status.
- The date and time of the choice.
- The consent version or configuration shown to the user.
- The categories selected.
- The mechanism used to collect the choice.
The exact retention approach should match the organisation’s legal and operational needs.
We should also plan for changes. If a website adds new trackers, changes purposes, or materially changes how technologies are used, the existing consent setup may need to be reviewed. The ICO specifically notes that fresh consent may be needed when cookie use changes.
A 2026 Compliance Lesson From Recent Enforcement
Recent enforcement shows that regulators are checking implementation, not just policy language. In 2024, CNIL reported 11 organisations were penalised for making cookie refusal harder than acceptance.
The ICO later reported that its assessment of the UK’s top 1,000 websites found 979 meeting its compliance checks at their most recent test, while 21 were still failing. The checks included whether advertising cookies were stored before users could choose and whether rejecting them was as easy as accepting them. The practical lesson is clear: a polished banner cannot compensate for a broken consent mechanism.
How to Audit a Cookie Banner
We can use a simple five-part audit:
1. Check Before Consent
Open the site without making a choice. Look for non-essential cookies, pixels, scripts, tags, and other tracking technologies.
2. Check the Refusal Path
Select the refusal option. Confirm that the relevant non-essential technologies remain blocked.
3. Check the Settings
Open the detailed preferences panel. Each category should be understandable, and choices should not be misleading.
4. Check Withdrawal
Find the privacy or consent control after making a choice. Users should have a practical way to change their decision.
5. Check Mobile
Repeat the process on a phone. A refusal option that is visible on desktop can become hidden or difficult to use on a smaller screen.
Conclusion
The strongest GDPR Cookie Banner is not simply the one that looks transparent. It is the one that behaves transparently. Recent regulatory work points to a practical standard: give users a real choice, respect that choice technically, and make refusal no harder than acceptance. Businesses that test the scripts behind their banner, keep their cookie inventory accurate, and review consent after website changes can address the part of cookie compliance that a banner alone cannot solve.
FAQ
Does every website need a GDPR Cookie Banner?
Not necessarily. The requirement depends on the technologies used, their purpose, applicable exemptions, and the laws applying to the website. Necessary technologies may qualify for an exception, while non-essential tracking generally needs a valid consent mechanism.
Is clicking “Accept” enough for Cookie Consent?
A click can provide the required positive action, but the surrounding information and choice must also meet the requirements for valid consent. Consent should be informed, specific, and freely given.
Can a website use “Accept” and “Manage Settings” without “Reject All”?
This design can create compliance concerns, particularly where refusal is harder than acceptance. Recent regulatory action shows that authorities are closely examining whether users can reject non-essential cookies as easily as they can accept them.
How often should Cookie Consent be reviewed?
We should review the banner whenever tracking technologies, purposes, vendors, or consent settings change. Regular technical scans are also useful because a website can become non-compliant after a new marketing or analytics script is added.
Leave a Reply