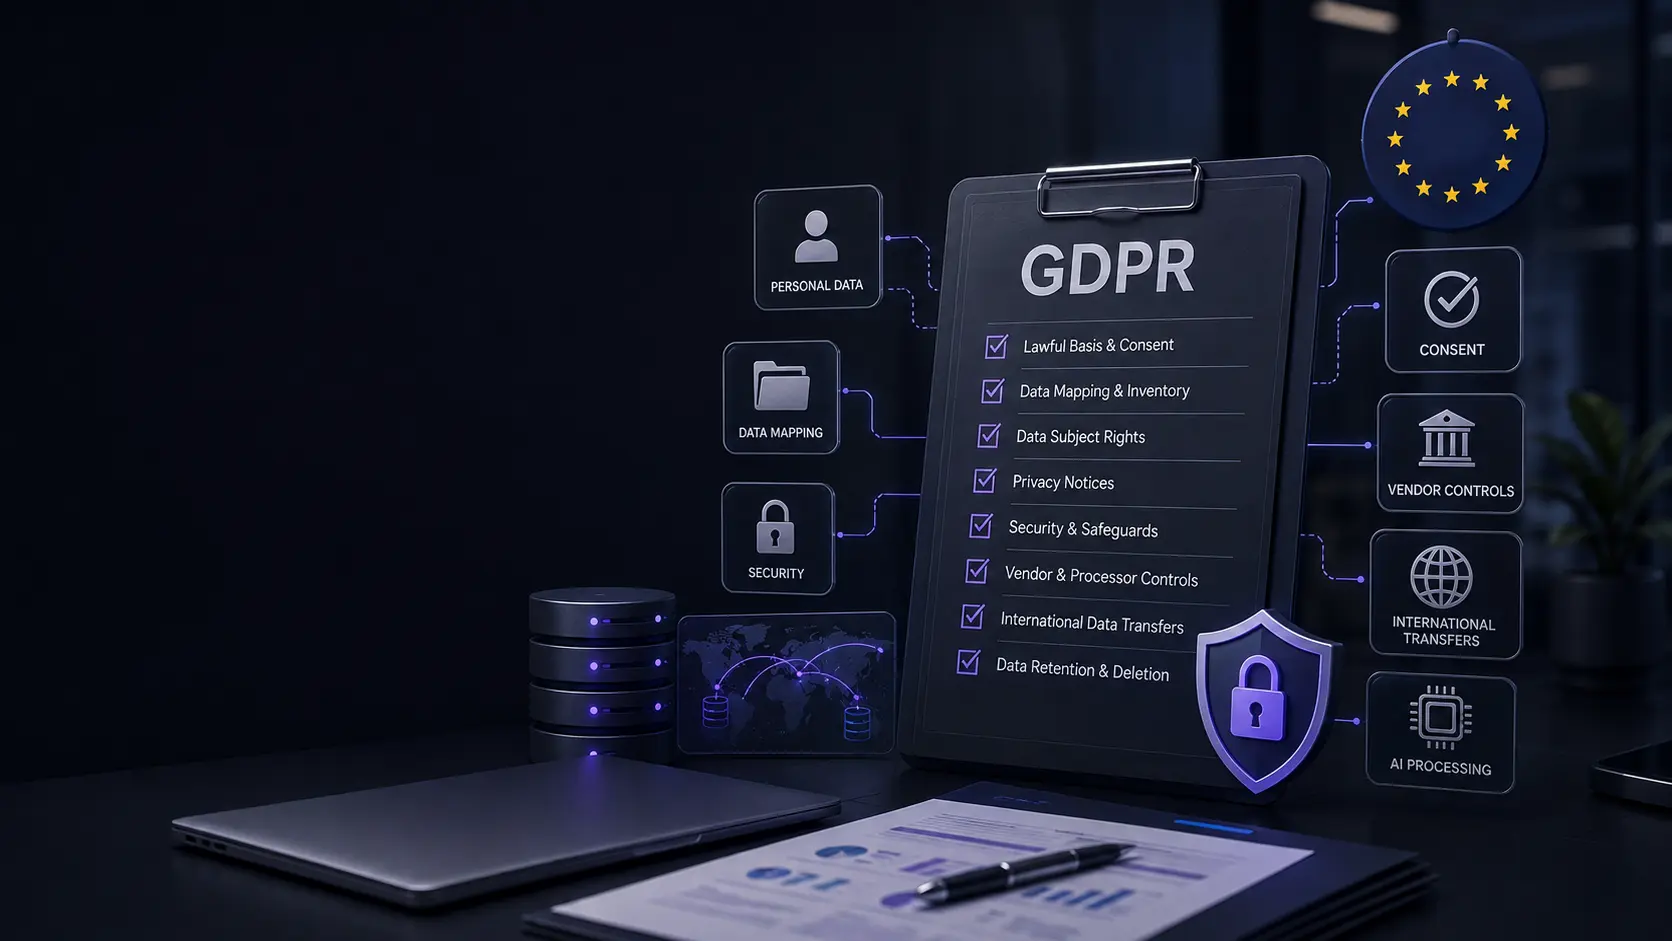
The most important GDPR requirement in 2026 is not simply having a privacy policy. Organisations need to prove what personal data they process, why they process it, where it goes, how long they keep it, and how they respond when a person exercises their rights. That practical proof is becoming more important as regulators focus on real implementation. The European Data Protection Board (EDPB) selected transparency and information duties as the subject of its 2026 coordinated enforcement action, involving 25 European data protection authorities. Recent enforcement also shows that basic rights can create real exposure. This gives businesses a useful way to approach GDPR requirements: treat compliance as an evidence system, not a document exercise.
What Are the Main GDPR Requirements?
The GDPR rules require organisations to build their data practices around several core principles. The European Commission identifies seven key principles, including lawfulness and transparency, purpose limitation, data minimisation, storage limitation, accuracy, security, and accountability.
1. Have a lawful reason for processing
Personal data processing needs a valid legal basis under Article 6. Depending on the activity, this can include consent, contract, legal obligation, vital interests, public task, or legitimate interests. The legal basis should be recorded for each processing activity. A vague statement such as “we use data to improve our services” may not explain enough about a specific use. For sensitive categories, such as health or biometric information, additional conditions can apply.
2. Collect only what you need
Data minimisation means organisations should avoid collecting personal information simply because it might become useful later. For example, an online booking form may need a customer’s name and contact details, but collecting unrelated information without a clear purpose creates another compliance burden.
3. Explain processing clearly
Privacy notices should tell people what data is collected, why it is used, the legal basis, who receives it, retention information, international transfers where relevant, and the rights available to the individual. This is especially important in 2026 because the EDPB’s coordinated enforcement work is examining transparency and information requirements under Articles 12, 13, and 14. A useful internal test is simple: Could an ordinary customer understand the data practice without asking your legal team?
The Overlooked GDPR Checklist: Map the Data, Not Just the Policy
A privacy policy cannot show everything an organisation actually does with personal data. A record of processing activities, often called a ROPA, provides a more useful operational view. Under Article 30, organisations may need records covering processing purposes, data categories, affected individuals, recipients, international transfers, retention periods where possible, and security measures.
Our practical checklist should therefore include:
- Data source: Where did the information come from?
- Purpose: Why is it being processed?
- Legal basis: What permits the processing?
- Recipients: Which vendors, teams, or partners receive it?
- Location: Does the data leave the European Economic Area?
- Retention: When should it be deleted?
- Security: What controls protect it?
- Rights process: How will access, deletion, objection, or correction requests be handled?
This mapping can expose problems that a privacy policy will not. For example, a company may have an accurate notice but discover that an old analytics platform still receives customer information.
GDPR Requirements for Vendors, AI, and International Transfers
Third-party tools deserve special attention. A business can remain responsible for its GDPR obligations even when another company processes the data. Contracts with processors should define their responsibilities, and organisations should know which vendors receive personal information. The European Commission also provides guidance covering processor relationships, data transfers, security, and other business obligations. International transfers also require care. EU data protection rules provide safeguards for transfers to third countries, including adequacy decisions, standard contractual clauses, and binding corporate rules.
This matters because GDPR protections are technology-neutral. Personal data remains protected whether it is processed through traditional software, automated systems, or newer AI applications.
Security and Breach Response Are Part of GDPR Compliance
GDPR rules require security measures that match the risks involved. Organisations should consider measures such as access controls, encryption where appropriate, backups, authentication, monitoring, and staff procedures.
A breach response plan should also be tested before an incident happens. Under Article 33, certain personal data breaches must be notified to the supervisory authority within 72 hours after becoming aware of the breach, unless the breach is unlikely to result in risks to people’s rights and freedoms. The key takeaway is that strong security measures and proper documentation must work together.
A business should be able to show what happened, which data was affected, when it discovered the incident, and what action it took.
GDPR Compliance Checklist for 2026
Use this short checklist for an annual review:
- Map every major personal data process.
- Record a lawful basis for each process.
- Review privacy notices for accuracy and clarity.
- Check consent mechanisms where consent is used.
- Review processor contracts and vendor access.
- Check international data transfers and safeguards.
- Set retention periods and deletion procedures.
- Test data subject rights procedures.
- Review security controls.
- Test the breach response process.
- Identify whether a Data Protection Impact Assessment (DPIA) must be conducted.
- Review AI tools, scraping activities, and automated processing.
- Keep evidence showing that controls actually operate.
Conclusion
The strongest GDPR requirements checklist for 2026 is built around evidence. A privacy notice matters, but it should match the systems, vendors, retention rules, rights procedures, security controls, and AI tools operating behind it. The latest enforcement direction reinforces that point. Regulators are examining whether organisations actually provide information and respect individual rights, while European guidance continues to address international transfers, security, and modern data processing. For businesses, the practical goal is straightforward: know your data, document why you use it, control where it goes, and be able to prove that your GDPR rules work in practice.
FAQ: Speech Disorder Data and GDPR
Yes. Information about a person’s health can fall within special category personal data under the GDPR when it reveals information about their health. Organisations handling such information need to consider both a lawful basis under Article 6 and an applicable condition under Article 9.
Yes, where the processing has an appropriate legal basis and satisfies the additional rules for special category data. The provider should collect only information needed for the stated purpose and protect it with suitable security controls.
It may be possible, but the organisation must assess the legal basis, purpose, recipient, contractual arrangements, and applicable safeguards before sharing it. The answer depends on the specific processing activity.
Leave a Reply